
Introduction
Welcome to the Cyphlens API documentation! You can use our API to access Cyphlens API endpoints, which can be used to enable and disable users for Cyphlens services, as well as create and verify 2FA Cyphlens images for different users.
All of our endpoints use the JSON data format to send and receive data.
We have language bindings in Shell, Python, and Java! You can view code examples in the dark area to the right, and you can switch the programming language of the examples with the tabs in the top right.
API base URL (sandbox): https://api.sandbox.cyphme.com/b2b/v1
API base URL (production): https://api.prod.cyphme.com/b2b/v1
Business Onboarding
Contact info@cyphlens.com to register your business with Cyphlens. You will need to provide the following:
- Company logo (in PNG format)
- Company name
- Company top level domain (TLD) where Cyphlens 2FA will be used
- Company server(s) IP address(es) to be whitelisted by Cyphlens
Cyphlens will then provide you with access to your business admin dashboard where you will be able find various settings, including your API credentials.
Authentication
Obtain an Access Token
curl -X POST "api_endpoint_url"
     -H "Authorization: Bearer <business_access_token>"
import requests

url = "api_endpoint_url"

headers = {
  'Content-Type': 'application/json',
  'Authorization': 'Bearer <business_access_token>'
}

response = requests.request("POST", url, json="", headers=headers)
Request request = new Request.Builder()
  .url("api_endpoint_here")
  .post("")
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer <business_access_token>")
  .build();
Cyphlens expects an Access Token to be included in the Authorization header of all API requests.
Given the API Client ID and Secret, an access token can be requested in two different ways as shown in the
following sections.
Get Access Token
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/auth/tokens"

headers = {
  'Authorization': 'Basic <Base64-encoded client_id:client_secret>'
}

response = requests.request("POST", url, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/auth/tokens"
     -H "Authorization: Basic <Base64-encoded client_id:client_secret>"
OkHttpClient client = new OkHttpClient();

Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/auth/tokens")
  .post(null)
  .addHeader("Authorization", "Basic <Base64-encoded client_id:client_secret>")
  .build();

Response response = client.newCall(request).execute();
This endpoint returns a business access token to be used as a Bearer token for all other API
requests. In order to request an Access Token using this method, you must include your Client ID and Secret in
the Authorization header using HTTP Basic authentication, as follows:
Authorization: Basic <Base64-encoded client_id:client_secret>
HTTP Request
POST /auth/tokens
Headers
Authorization: Basic <Base64-encoded client_id:client_secret>
Content-Type: application/json
Request body
-- NONE --
Response body (on success)
{
  "businessId": "8871918765655860884",
  "token": "5c8e744eac7f44e6a1462bfXXXXXXXX",
  "expiresAt": 1564242383612
}
Error Response Examples
{
  "status": "401",
  "error": "Unauthorized",
  "message": "Invalid client id or secret",
  "path": "/b2b/v1/auth/tokens",
  "timestamp": "2024-03-25T10:33:11.857+0000"
}
{
  "status": "401",
  "error": "Unauthorized",
  "message": "Invalid IP address",
  "path": "/b2b/v1/auth/tokens",
  "timestamp": "2024-03-25T10:33:11.857+0000"
}
Response Parameters
| Parameter | Description |
|---|---|
| businessId | Unique ID of your business. |
| token | The business access token to use in all other API requests. Once expired, it needs to be renewed. |
| expiresAt | Token expiration time in milliseconds - UTC time. |
Get Access Token (OAuth 2.0 compatible)
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/oauth/tokens"
headers = {
  "Authorization": "Basic <Base64-encoded client_id:client_secret>",
  "Content-Type": "application/x-www-form-urlencoded",
}

data = "grant_type=client_credentials&scope=api%3Aread+api%3Awrite"  # scope is optional

response = requests.request("POST", url, headers=headers, data=data)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/oauth/tokens" \
  -H "Authorization: Basic <Base64-encoded client_id:client_secret>" \
  -H "Content-Type: application/x-www-form-urlencoded" \
  -d "grant_type=client_credentials&scope=api%3Aread+api%3Awrite"
OkHttpClient client = new OkHttpClient();

RequestBody body = RequestBody.create(
  "grant_type=client_credentials&scope=api%3Aread+api%3Awrite",
  MediaType.parse("application/x-www-form-urlencoded")
);

Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/oauth/tokens")
  .post(body)
  .addHeader("Authorization", "Basic <Base64-encoded client_id:client_secret>")
  .addHeader("Content-Type", "application/x-www-form-urlencoded")
  .build();

Response response = client.newCall(request).execute();
This endpoint returns an OAuth 2.0 compatible access token using the client_credentials grant
type. The returned token can be used as a Bearer token in the Authorization header of
all other API requests.
In order to request an Access Token using this method, you must include your API Client ID and Secret in the
Authorization header using HTTP Basic authentication, as follows:
Authorization: Basic <Base64-encoded client_id:client_secret>
HTTP Request
POST /oauth/tokens
Headers
Authorization: Basic <Base64-encoded client_id:client_secret>
Content-Type: application/x-www-form-urlencoded
Request body
grant_type=client_credentials&scope=api%3Aread+api%3Awrite // scope is optional
Response body (on success)
{
  "business_id": "8871918765655860884",
  "access_token": "5c8e744eac7f44e6a1462bfXXXXXXXX",
  "token_type": "Bearer",
  "expires_in": 3600, // Token validity duration in seconds
  "scope": "api:read api:write" // Token scope (if provided in request)
}
Request Parameters
| Parameter | Description |
|---|---|
| grant_type | OAuth 2.0 grant type |
| scope | API permissions scope (optional) |
Response Parameters
| Parameter | Description |
|---|---|
| business_id | Unique ID of your business. |
| access_token | The business access token to use in all other API requests. Once expired, it needs to be renewed. |
| token_type | The type of the returned token. For this endpoint it will always be Bearer. |
| expires_in | Token validity duration in seconds. |
| scope | API read/write permissions for the given access token. |
Users
Enable Your User for Cyphlens Services
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/users"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}
payload = {
  'action': 'ADD',            // ADD, DELETE, HARD_DELETE
  'emails': ['user1@business.com', 'user2@business.com', 'gmail.com']
}

response = requests.request("POST", url, json=payload, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/users"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
     -d '{
           "action": "ADD",            // ADD, DELETE, HARD_DELETE
           "emails": ["user1@business.com", "user2@business.com", "gmail.com"]
     }'
OkHttpClient client = new OkHttpClient();

MediaType mediaType = MediaType.parse("application/json");

JSONObject jsonObject = new JSONObject();
jsonObject.put("action", "ADD");            // ADD, DELETE, HARD_DELETE
jsonObject.put("emails", new JSONArray(new String[]{"user1@business.com", "user2@business.com", "gmail.com"}));

RequestBody body = RequestBody.create(mediaType, jsonObject.toString());
Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/users")
  .post(body)
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint enables Cyphlens services (e.g., 2FA) for a user. After a user is enabled, if they signed up in the Cyphlens app with a different email address, they will receive an email with a linking token in order to link their existing Cyphlens account to the email address used in this API call.
HTTP Request
POST /users
Headers
Authorization: Bearer <business_access_token>
Request body
{
  "action": "ADD",
  "emails": [
    "user1@business.com",
    "user2@business.com",
    "gmail.com"
  ]
}
Request Parameters
| Parameter | Description |
|---|---|
| action | Currently supported action: ADD |
| emails | The list of users to enable for Cyphlens services |
Response body (on success)
{
  "added": [
    {
      "id": "3891926237655860884",
      "status": "PENDING", // ACTIVE, PENDING
      "linkStatus": "PENDING", // ACCEPTED, PENDING, EXPIRED
      "email": "user1@business.com",
      "createdAt": 1724337339000 // UTC time
    }
  ],
  "invalid": [
    {
      "email": "user2@business.com",
      "reason": "USER_ALREADY_EXISTS"
    },
    {
      "email": "gmail.com",
      "reason": "INVALID_EMAIL_ADDRESS" // OTHER_LINKING_PENDING
    }
  ]
}
Error Response Examples
{
  "status": "401",
  "error": "Unauthorized",
  "message": "Invalid access token",
  "path": "/b2b/v1/users",
  "timestamp": "2024-03-25T10:33:11.857+0000"
}
{
  "status": "401",
  "error": "Unauthorized",
  "message": "Invalid IP address",
  "path": "/b2b/v1/users",
  "timestamp": "2024-03-25T10:33:11.857+0000"
}
Response Parameters
| Parameter | Description |
|---|---|
| action | Action performed to the following list of users |
| ↳ id | Unique ID of the user |
| ↳ status | User account status after the action |
| ↳ linkStatus | User linking status to the business (whether enabled or not for the business) |
| User account being enabled for your business | |
| ↳ createdAt | Timestamp of when this user was enabled for your business |
| invalid | List of users who could not be enabled for your business |
| Email address of the user that could not be enabled | |
| ↳ reason | Human readable reason on why the user could not be enabled |
Disable Cyphlens Services For Users (bulk actions)
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/users/bulk"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}
payload = {
  'action': 'DELETE', # DELETE, HARD_DELETE, RESTORE
  'emails': ['user1@business.com', 'user2@business.com']
}

response = requests.request("POST", url, json=payload, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/users/bulk"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
     -d '{
           "action": "DELETE",
           "emails": ["user1@business.com", "user2@business.com"]
     }'
OkHttpClient client = new OkHttpClient();

MediaType mediaType = MediaType.parse("application/json");

JSONObject jsonObject = new JSONObject();
jsonObject.put("action", "DELETE");            // DELETE, HARD_DELETE, RESTORE
jsonObject.put("emails", new JSONArray(new String[]{"user1@business.com", "user2@business.com"}));

RequestBody body = RequestBody.create(mediaType, jsonObject.toString());
Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/users/bulk")
  .post(body)
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint disables all Cyphlens services (e.g., 2FA) for your end-users.
HTTP Request
POST /users/bulk
Headers
Authorization: Bearer <business_access_token>
Request body
{
  "action": "DELETE", // DELETE, HARD_DELETE, RESTORE
  "emails": [
    "user1@business.com",
    "user2@business.com"
  ]
}
Request Parameters
| Parameter | Description |
|---|---|
| action | Currently supported actions: DELETE, HARD_DELETE, RESTORE |
| emails | The list of users to apply this action to |
Response body (on success)
{
  "deleted": [
    {
      "id": "3891926237655860884",
      "status": "INACTIVE", // INACTIVE, DELETED
      "email": "user1@business.com",
      "updatedAt": 1724337399000
    }
  ],
  "invalid": [
    {
      "email": "user2@business.com",
      "reason": "USER_NOT_FOUND"
    }
  ]
}
Response Parameters
| Parameter | Description |
|---|---|
| deleted | Action performed to the following list of users |
| ↳ id | Unique ID of the user |
| ↳ status | User account status after the action |
| User account being enabled for your business | |
| ↳ createdAt | Timestamp of when this user was enabled for your business |
| invalid | List of users who could not be enabled for your business |
| Email address of the user that could not be enabled | |
| ↳ reason | Human readable reason on why the user could not be enabled |
Disable Cyphlens Services For A User (single user)
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}

response = requests.request("DELETE", url, headers=headers)
curl -X DELETE "https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
OkHttpClient client = new OkHttpClient();

Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884")
  .delete(null)
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint disables all Cyphlens services (e.g., 2FA) for your end-user. This is equivalent
to the DELETE action in the previous bulkendpoint.
HTTP Request
DELETE /users/{userId}
Headers
Authorization: Bearer <business_access_token>
Request body
-- NONE --
Response body (on success)
{
  "id": "3891926237655860884",
  "status": "INACTIVE",
  "email": "user@business.com",
  "updatedAt": 1724337399000
}
Response Parameters
| Parameter | Description |
|---|---|
| id | Unique ID of the user |
| status | User account status after the action |
| User account being disabled | |
| updatedAt | Timestamp of when this user account was disabled |
Search User Account Information by Email
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/users/search"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}
payload = {
  'email': 'user@business.com'
}

response = requests.request("POST", url, json=payload, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/users/search"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
     -d '{
           "email": "user@business.com"
     }'
OkHttpClient client = new OkHttpClient();

MediaType mediaType = MediaType.parse("application/json");

JSONObject jsonObject = new JSONObject();
jsonObject.put("email", "user@business.com");

RequestBody body = RequestBody.create(mediaType, jsonObject.toString());
Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/users/search")
  .post(body)
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint returns the user account information, including the account status.
HTTP Request
POST /users/search
Request body
{
  "email": "user@business.com"
}
Request Parameters
| Parameter | Description |
|---|---|
| User email address |
Response body (on success)
{
  "id": "3891926237655860884",
  "status": "ACTIVE", // ACTIVE, PENDING, INACTIVE
  "linkStatus": "ACCEPTED", // ACCEPTED, PENDING, EXPIRED
  "recoveryContactStatus": "INACTIVE", // ACCEPTED, PENDING, EXPIRED, INACTIVE
  "firstName": "John", // Return only if status ACTIVE
  "lastName": "Doe", // Return only if status ACTIVE
  "email": "user@business.com",
  "createdAt": 1724337339000,
  "updatedAt": 1724337399000
}
Response Parameters
| Parameter | Description |
|---|---|
| id | Unique ID of the user |
| status | User account status |
| linkStatus | User linking status to the business (whether enabled or not for Cyphlens services) |
| recoveryContactStatus | Whether or not the user has a valid recovery contact for their Cyphlens account |
| firstName | The user first name |
| lastName | The user last name |
| User email address being used for the business | |
| createdAt | Timestamp of when this user account was enabled for Cyphlens services |
| updatedAt | Timestamp of when this user account was last updated |
Get User Account Information by ID
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}

response = requests.request("GET", url, headers=headers)
curl -X GET "https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
OkHttpClient client = new OkHttpClient();

Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/users/3891926237655860884")
  .get()
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint returns the user account information, including the account status.
HTTP Request
GET /users/{userId}
Headers
Authorization: Bearer <business_access_token>
Request body
-- NONE --
Response body (on success)
{
  "id": "3891926237655860884",
  "status": "PENDING", // ACTIVE, PENDING, INACTIVE
  "linkStatus": "EXPIRED", // ACCEPTED, PENDING, EXPIRED
  "recoveryContactStatus": "ACCEPTED", // ACCEPTED, PENDING, EXPIRED, INACTIVE
  "firstName": "John", // Return only if status ACTIVE
  "lastName": "Doe", // Return only if status ACTIVE
  "email": "user@business.com",
  "createdAt": 1724337339000,
  "updatedAt": 1724337399000
}
Response Parameters
| Parameter | Description |
|---|---|
| id | Unique ID of the user |
| status | User account status after the action |
| linkStatus | User linking status to the business (whether enabled or not for the business) |
| recoveryContactStatus | Whether or not the user has a valid recovery contact for their Cyphlens account |
| firstName | The user first name |
| lastName | The user last name |
| User email address being used for the business | |
| createdAt | Timestamp of when this user account was enabled forCyphlens services |
| updatedAt | Timestamp of when this user account was last updated |
Cyphlens Images
Display a Cyphlens Image
<head>
    ...
    // Cyphlens Backend API Callback Fragment
    if (data.imageType === 'SVG') {
        $scope.imageURL = 'data:image/svg+xml;base64,' + data.image;
    } else {
        $scope.imageURL = 'data:image/png+xml;base64,' + data.image;
    }
    $scope.sessionId = data.sessionId;
    ...
</head>


<body>
    ...
    <div class="form_wrapper">
        ...
	// Make a Cyphlens image open directly in the mobile app
        <a href="cyphme://mobile.sandbox.cyphme.com/documents/file?sid={{sessionId}}">">
            <div class="cyphlens-image">
                <img id="svg" height="210px" ng-src="{{imageURL}}"/>
            </div>
        </a>
        ...
    </div>
    ...
</body>
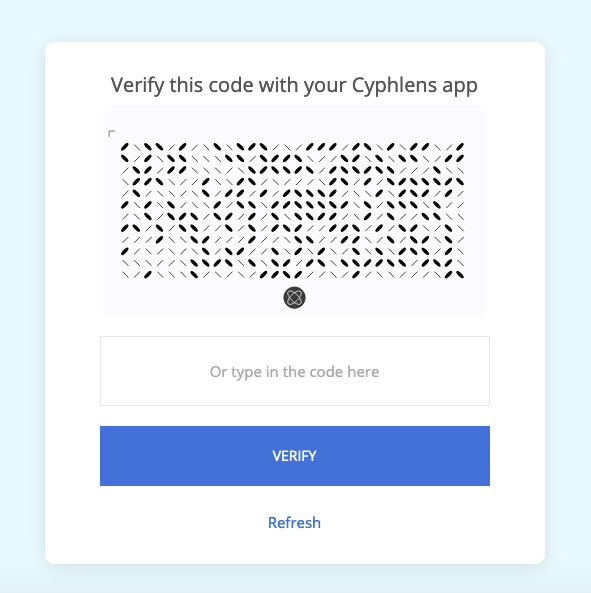
The sample code displayed to the right can be used to include a Cyphlens Image in a webpage as shown in the screenshot below.
Cyphlens Image Deeplink (mobile-only user experience)
In order to enable a mobile-only user experience with Cyphlens 2FA, wrap the 2FA Cyphlens image in an HTML
<a> tag with an href value equal to the URL below where the query parameter
sessionId is the session ID received in the response to the /auth/login endpoint.
Sandbox
cyphme-sandbox://www.cyphme.com/verifydocument?sessionId=394bf15a889c47ad8b7bcfaedb38xxxx
Production
cyphme://www.cyphme.com/verifydocument?sessionId=394bf15a889c47ad8b7bcfaedb38xxxx
2FA Endpoints
Create a 2FA Cyphlens Image For a User
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/auth/login"

headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}
payload = {
  'url': 'dashboard.business.com',
  'email': 'user@business.com',
  'imageType': 'SVG'
}

response = requests.request("POST", url, json=payload, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/auth/login"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
     -d '{
           "url": "dashboard.business.com",
           "email": "user@business.com",
           "imageType": "SVG"
     }'
OkHttpClient client = new OkHttpClient();

MediaType mediaType = MediaType.parse("application/json");

JSONObject jsonObject = new JSONObject();
jsonObject.put("url", "dashboard.business.com");
jsonObject.put("email", "user@business.com");
jsonObject.put("imageType", "SVG");

RequestBody body = RequestBody.create(mediaType, jsonObject.toString());
Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/auth/login")
  .post(body)
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint generates a 2FA Cyphlens Image for a specific user.
HTTP Request
POST /auth/login
Headers
Authorization: Bearer <business_access_token>
Request body
{
  "url": "dashboard.business.com", // URL for 2FA delegation
  "email": "user@business.com", // Email address of the user doing the 2FA challenge
  "imageType": "SVG" // SVG, PNG
}
Request Parameters
| Parameter | Description |
|---|---|
| url | The URL of the website for which the Cyphlens 2FA challenge is being generated |
| User account requesting the Cyphlens 2FA challenge | |
| imageType | Format of the Cyphlens 2FA image being returned (SVG recommended for the web) |
Response body (on success)
{
  "sessionId": "64feea50a4444ac49b7c02cb348f4810",
  "challenge": {
    "type": "IMAGE",
    "format": "SVG",
    "data": "PHN2ZyBiYXN1LNB...Zm9ybWF0PSJ0aW4uLi4u",
    "expiresAt": 1724756604856 // UTC time
  }
}
Response Parameters
| Parameter | Description |
|---|---|
| sessionId | Unique session ID for this 2FA Cyphlens challenge request |
| challenge | Cyphlens 2FA challenge details |
| ↳ type | Type of the 2FA Cyphlens challenge (currently only IMAGE is supported) |
| ↳ format | Format of the Cyphlens 2FA image being returned (as requested in the imageType request parameter) |
| ↳ data | Base64 encoded Cyphlens 2FA image data |
| ↳ expiresAt | Timestamp in UTC time representing the expiration date and time of the Cyphlens 2FA challenge (default is 60 seconds) |
Verify a 2FA Cyphlens Image With PIN
import requests

url = "https://api.sandbox.cyphme.com/b2b/v1/auth/verify"
headers = {
  'Authorization': 'Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX'
}
payload = {
  'email': 'user@business.com',
  'passcode': '123456',
  'sessionId': '64feea50a4444ac49b7c02cb348f4810'
}

response = requests.request("POST", url, json=payload, headers=headers)
curl -X POST "https://api.sandbox.cyphme.com/b2b/v1/auth/verify"
     -H "Authorization: Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX"
     -d '{
           "email": "user@business.com",
           "passcode": "123456",
           "sessionId": "64feea50a4444ac49b7c02cb348f4810"
     }'
OkHttpClient client = new OkHttpClient();

MediaType mediaType = MediaType.parse("application/json");

JSONObject jsonObject = new JSONObject();
jsonObject.put("email", "user@business.com");
jsonObject.put("passcode", "123456");
jsonObject.put("sessionId", "64feea50a4444ac49b7c02cb348f4810");

RequestBody body = RequestBody.create(mediaType, jsonObject.toString());
Request request = new Request.Builder()
  .url("https://api.sandbox.cyphme.com/b2b/v1/auth/verify")
  .post(body)
  .addHeader("Content-Type", "application/json")
  .addHeader("Authorization", "Bearer 5c8e744eac7f44e6a1462bfXXXXXXXX")
  .build();

Response response = client.newCall(request).execute();
This endpoint verifies the Cyphlens 2FA challenge with the passcode decrypted from the corresponding Cyphlens image for a specific session and a specific user.
HTTP Request
POST /auth/verify
Headers
Authorization: Bearer <business_access_token>
Request body
{
  "email": "user@business.com",
  "passcode": "123456",
  "sessionId": "64feea50a4444ac49b7c02cb348f4810"
}
Request Parameters
| Parameter | Description |
|---|---|
| User account requesting the Cyphlens 2FA challenge | |
| passcode | Unique 6 digit OTP as decrypted by the user from the Cyphlens 2FA image |
| sessionId | Unique session ID for this 2FA Cyphlens challenge |
Response body (on success)
{
  "userId": "3891926237655860884",
  "status": "SUCCESS"
}
Response Parameters
| Parameter | Description |
|---|---|
| userId | Unique user ID of the user performing the 2FA Cyphlens challenge |
| status | Cyphlens 2FA challenge status |
Errors
The Cyphlens API uses the following error codes:
| Error Code | Meaning |
|---|---|
| 400 | Bad Request -- Your request has some invalid or missing data. |
| 401 | Unauthorized -- Either your API key is wrong, your access token is wrong or your IP address is invalid. |
| 404 | Not Found -- The specified end-user could not be found. |
| 405 | Method Not Allowed -- You tried to access the Cyphlens API with an invalid method. |
| 406 | Not Acceptable -- You requested a format that is not well-formed JSON |
| 429 | Too Many Requests -- You're sending too many requests! Slow down! |
| 500 | Internal Server Error -- We had a problem with our server. Try again later. |